The vCenter alarm ESXi Host Certificate Status fires about 30 days before an ESXi host certificate in VECS expires. The quickest fix is in the vSphere Client: select the host, open Configure → System → Certificate and click Renew (on vCenter 8.0 Update 3 and later, click MANAGE WITH VMCA first). From vCenter 8.0 Update 3h and VCF 9.0.2, VMCA-issued ESXi certificates renew themselves automatically, as long as the certificate mode is vmca.
Before you renew
- The VMCA root certificate is not expired (Administration → Certificate Management → Trusted Root).
- The vCenter Machine SSL certificate is valid.
- The host is connected (green) in vCenter, and time sync and DNS resolution work.
- On vCenter versions before 8.0 Update 3, take the host out of maintenance mode first.
Source: Broadcom KB 374032 (ESXi 7.x, 8.x and 9.x).
Renew the certificate in the vSphere Client
| vCenter version | Steps |
|---|---|
| 8.0 Update 3 and later | Host → Configure → System → Certificate → MANAGE WITH VMCA → Renew |
| Earlier versions | Host → Configure → System → Certificate → Renew or Refresh CA Certificates |
For many hosts at once, a PowerCLI loop is faster; see ESXi Host Certificate Status alarm bulk resolution on Enterprise Admins.
Automatic renewal in 8.0 U3h and VCF 9.0.2
- From vCenter 8.0 Update 3h and VCF 9.0.2, VMCA-issued ESXi certificates renew automatically 10 days before expiry. The threshold is adjustable with the vCenter advanced setting
vpxd.certmgmt.certs.autoRenewThreshold. - The vCenter Machine SSL certificate renews 5 days before expiry, without a service restart.
- Auto-renewal does not work when
vpxd.certmgmt.modeiscustom; it must bevmca.
Source: Broadcom KB 427937.
Why the 30-day alarm usually fires before the 10-day native renewal, and how the vCenter, ESXi and Fleet Management renewal mechanisms differ, is covered in vCenter Certificate Auto-Renewal: When You Still Need vCert. In VCF 9, giving hosts CA-signed certificates through Fleet Management switches vCenter to custom mode, which turns native renewal off and changes how new hosts are onboarded: see VCF 9 Certificate Management: Custom CAs, Auto-Renewal, and Host Onboarding.
When the vSphere Client isn’t enough: vCert
If the host has already disconnected, or trust between vCenter and the host is broken after a CA change, use option 7 (ESXi certificate operations) in vCert. It validates the trust between vCenter and ESXi, checks database consistency, and replaces rui.crt, rui.key and castore.pem.
Check the certificate on the host
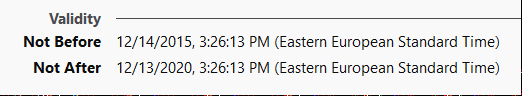
You can see the current certificate and its expiry when you log in to the ESXi host:
Last resort: regenerate a self-signed certificate on the host
Generating new certificates by hand is normally needed only if you changed the host name or accidentally deleted the certificate. Log in to the host over SSH, in maintenance mode:
cd /etc/vmware/ssl
mv rui.crt orig.rui.crt
mv rui.key orig.rui.key

/sbin/generate-certificates

reboot
This produces a self-signed certificate. Afterwards, renew the host from vCenter so it gets a VMCA-signed certificate again, or replace it with a trusted certificate from your CA.