vCenter Upgrade Download: ISO and Patch Files for Every 8.0 and 9.x Build

Which vCenter file to download for an upgrade or patch (full VCSA ISO or patch-FP.iso), where it is on the Broadcom portal, and every 8.0 and 9.x build.

Short answer: For a vCenter update within the same major version (for example 8.0 U2 to 8.0 U3k) download the patch ISO (…-patch-FP.iso) from Broadcom Support Portal > My Downloads > Solutions and install it from the VAMI. For a new install or a major upgrade (7.0 to 8.0, 8.0 to 9.0) download the full installer ISO (VMware-VCSA-all-…iso) from My Downloads > Products. The download list below gives every vCenter 7.0, 8.0 and 9.x build with its patch ISO file name.

Which vCenter file do you need?

FileName patternUse it for
Full installer ISOVMware-VCSA-all-<x.y.z>-<build>.isoNew install, major upgrade (7.0 to 8.0, 8.0 to 9.0) and migration. The installer deploys a new appliance and copies the configuration and data from the old one.
Patch ISOVMware-vCenter-Server-Appliance-<version>-<build>-patch-FP.isoUpdate or patch within the same major version (for example 8.0 U2 to 8.0 U3k). Attach it to the appliance CD-ROM and install it from the VAMI or with software-packages.
Update repositoryVMware-vCenter-Server-Appliance-<version>-<build>-updaterepo.zipPublished for some releases. Unzip it on an internal web server and point the VAMI update settings at that URL.

A version appears in the portal only if your account has an entitlement for it, and the portal asks you to sign in first. For the ESXi side of the same upgrade see the ESXi ISO download list.

vCenter download list: every build for 7.0, 8.0 and 9.x

Builds and dates from Broadcom KB 326316, checked on 30 September 2026. The patch ISO names follow Broadcom’s fixed pattern, which I checked against eleven real downloads from 7.0 U1c to 8.0 U3b. A GA release is the base version, so it has only a full installer ISO. Each link opens the Broadcom Support Portal.

vCenter 9.x (9 releases)
ReleaseBuildRelease dateDownload
vCenter 9.1.1.0257128392026-09-03Broadcom portal
vCenter 9.1.0.0300256295302026-07-29Broadcom portal
vCenter 9.1.0.0200255736142026-07-13Broadcom portal
vCenter 9.1.0.0100254179262026-06-05Broadcom portal
vCenter 9.1253709222026-05-12Broadcom portal
vCenter 9.0.2.0100256295252026-07-29Broadcom portal
vCenter 9.0.2.0251480862026-01-20Broadcom portal
vCenter 9.0.1.0249574542025-09-29Broadcom portal
vCenter 9.0.0.0247552302025-06-17Broadcom portal
vCenter 8.0 (28 releases)
ReleaseBuildRelease datePatch ISO
8.0 U3k256004172026-07-29VMware-vCenter-Server-Appliance-8.0.3.01000-25600417-patch-FP.iso
8.0 U3j254133642026-05-27VMware-vCenter-Server-Appliance-8.0.3.00900-25413364-patch-FP.iso
8.0 U3i251973302026-02-24VMware-vCenter-Server-Appliance-8.0.3.00800-25197330-patch-FP.iso
8.0 U3h250927192025-12-15VMware-vCenter-Server-Appliance-8.0.3.00700-25092719-patch-FP.iso
8.0 U3g248536462025-07-29VMware-vCenter-Server-Appliance-8.0.3.00600-24853646-patch-FP.iso
8.0 U3e246743462025-04-11VMware-vCenter-Server-Appliance-8.0.3.00500-24674346-patch-FP.iso
8.0 U3d243228312024-10-21VMware-vCenter-Server-Appliance-8.0.3.00400-24322831-patch-FP.iso
8.0 U3c243051612024-10-09VMware-vCenter-Server-Appliance-8.0.3.00300-24305161-patch-FP.iso
8.0 U3b242623222024-09-17VMware-vCenter-Server-Appliance-8.0.3.00200-24262322-patch-FP.iso
8.0 U3a240911602024-07-18VMware-vCenter-Server-Appliance-8.0.3.00100-24091160-patch-FP.iso
8.0 U3240225152024-06-25VMware-vCenter-Server-Appliance-8.0.3.00000-24022515-patch-FP.iso
8.0 U2f256243212026-08-03VMware-vCenter-Server-Appliance-8.0.2.00600-25624321-patch-FP.iso
8.0 U2e243216532024-10-21VMware-vCenter-Server-Appliance-8.0.2.00500-24321653-patch-FP.iso
8.0 U2d239291362024-06-17VMware-vCenter-Server-Appliance-8.0.2.00400-23929136-patch-FP.iso
8.0 U2c235043902024-03-26VMware-vCenter-Server-Appliance-8.0.2.00300-23504390-patch-FP.iso
8.0 U2b233199932024-03-04VMware-vCenter-Server-Appliance-8.0.2.00200-23319993-patch-FP.iso
8.0 U2a226172212023-10-26VMware-vCenter-Server-Appliance-8.0.2.00100-22617221-patch-FP.iso
8.0 U2223857392023-09-21VMware-vCenter-Server-Appliance-8.0.2.00000-22385739-patch-FP.iso
8.0 U1e240051652024-06-12VMware-vCenter-Server-Appliance-8.0.1.00500-24005165-patch-FP.iso
8.0 U1d223680472023-10-24VMware-vCenter-Server-Appliance-8.0.1.00400-22368047-patch-FP.iso
8.0 U1c220889812023-07-27VMware-vCenter-Server-Appliance-8.0.1.00300-22088981-patch-FP.iso
8.0 U1b218605032023-06-22VMware-vCenter-Server-Appliance-8.0.1.00200-21860503-patch-FP.iso
8.0 U1a218150932023-06-01VMware-vCenter-Server-Appliance-8.0.1.00100-21815093-patch-FP.iso
8.0 U1215604802023-04-18VMware-vCenter-Server-Appliance-8.0.1.00000-21560480-patch-FP.iso
8.0c214573842023-03-30VMware-vCenter-Server-Appliance-8.0.0.10300-21457384-patch-FP.iso
8.0b212160662023-02-14VMware-vCenter-Server-Appliance-8.0.0.10200-21216066-patch-FP.iso
8.0a209203232022-12-16VMware-vCenter-Server-Appliance-8.0.0.10100-20920323-patch-FP.iso
8.0 GA205195282022-10-11Full ISO only
vCenter 7.0 (37 releases)
ReleaseBuildRelease datePatch ISO
7.0 U3w249270112025-09-29VMware-vCenter-Server-Appliance-7.0.3.02500-24927011-patch-FP.iso
7.0 U3v247302812025-05-20VMware-vCenter-Server-Appliance-7.0.3.02400-24730281-patch-FP.iso
7.0 U3u246142102025-04-01VMware-vCenter-Server-Appliance-7.0.3.02300-24614210-patch-FP.iso
7.0 U3t243220182024-10-21VMware-vCenter-Server-Appliance-7.0.3.02200-24322018-patch-FP.iso
7.0 U3s242019902024-09-17VMware-vCenter-Server-Appliance-7.0.3.02100-24201990-patch-FP.iso
7.0 U3r240266152024-06-17VMware-vCenter-Server-Appliance-7.0.3.02000-24026615-patch-FP.iso
7.0 U3q237880362024-05-21VMware-vCenter-Server-Appliance-7.0.3.01900-23788036-patch-FP.iso
7.0 U3p228373222023-12-07VMware-vCenter-Server-Appliance-7.0.3.01800-22837322-patch-FP.iso
7.0 U3o223576132023-09-28VMware-vCenter-Server-Appliance-7.0.3.01700-22357613-patch-FP.iso
7.0 U3n219584062023-07-07VMware-vCenter-Server-Appliance-7.0.3.01600-21958406-patch-FP.iso
7.0 U3m217842362023-06-22VMware-vCenter-Server-Appliance-7.0.3.01500-21784236-patch-FP.iso
7.0 U3l214777062023-03-30VMware-vCenter-Server-Appliance-7.0.3.01400-21477706-patch-FP.iso
7.0 U3k212904092023-02-23VMware-vCenter-Server-Appliance-7.0.3.01300-21290409-patch-FP.iso
7.0 U3j209900772022-12-22VMware-vCenter-Server-Appliance-7.0.3.01200-20990077-patch-FP.iso
7.0 U3i208452002022-12-08VMware-vCenter-Server-Appliance-7.0.3.01100-20845200-patch-FP.iso
7.0 U3h203950992022-09-13VMware-vCenter-Server-Appliance-7.0.3.01000-20395099-patch-FP.iso
7.0 U3g201505882022-07-23VMware-vCenter-Server-Appliance-7.0.3.00800-20150588-patch-FP.iso
7.0 U3f200514732022-07-12VMware-vCenter-Server-Appliance-7.0.3.00700-20051473-patch-FP.iso
7.0 U3e197174032022-05-12VMware-vCenter-Server-Appliance-7.0.3.00600-19717403-patch-FP.iso
7.0 U3d194808662022-03-29VMware-vCenter-Server-Appliance-7.0.3.00500-19480866-patch-FP.iso
7.0 U3c192345702022-01-27VMware-vCenter-Server-Appliance-7.0.3.00300-19234570-patch-FP.iso
7.0 U3a187784582021-10-21VMware-vCenter-Server-Appliance-7.0.3.00100-18778458-patch-FP.iso
7.0 U3187004032021-10-05VMware-vCenter-Server-Appliance-7.0.3.00000-18700403-patch-FP.iso
7.0 U2d184551842021-09-21VMware-vCenter-Server-Appliance-7.0.2.00500-18455184-patch-FP.iso
7.0 U2c183563142021-08-24VMware-vCenter-Server-Appliance-7.0.2.00400-18356314-patch-FP.iso
7.0 U2b179584712021-05-25VMware-vCenter-Server-Appliance-7.0.2.00200-17958471-patch-FP.iso
7.0 U2a179201682021-04-27VMware-vCenter-Server-Appliance-7.0.2.00100-17920168-patch-FP.iso
7.0 U2176948172021-03-09VMware-vCenter-Server-Appliance-7.0.2.00000-17694817-patch-FP.iso
7.0 U1d174911012021-02-02VMware-vCenter-Server-Appliance-7.0.1.00300-17491101-patch-FP.iso
7.0 U1c173275172020-12-17VMware-vCenter-Server-Appliance-7.0.1.00200-17327517-patch-FP.iso
7.0 U1a170049972020-10-22VMware-vCenter-Server-Appliance-7.0.1.00100-17004997-patch-FP.iso
7.0 U1168601382020-10-06VMware-vCenter-Server-Appliance-7.0.1.00000-16860138-patch-FP.iso
7.0.0d167496532020-08-25VMware-vCenter-Server-Appliance-7.0.0.10700-16749653-patch-FP.iso
7.0.0c166200072020-07-30VMware-vCenter-Server-Appliance-7.0.0.10600-16620007-patch-FP.iso
7.0.0b163862922020-06-23VMware-vCenter-Server-Appliance-7.0.0.10400-16386292-patch-FP.iso
7.0.0a161890942020-05-19VMware-vCenter-Server-Appliance-7.0.0.10300-16189094-patch-FP.iso
7.0 GA159524982020-04-02Full ISO only

In VCF 9, SDDC Manager and VCF Operations fleet management usually download the vCenter upgrade bundles through their depot, so you rarely fetch a vCenter file by hand. A standalone vCenter 9 in vSphere Foundation is patched from the VAMI as before.

Full installer ISO file names for vCenter 8.0 and 9.x

Broadcom does not publish a full installer ISO for every patch, so only the releases below have one. The names are confirmed from real downloads. In 8.0 the name uses the update level and the build (8.0.3-24853646); from 9.0 it uses the full four-part version and a dot before the build (9.1.0.0300.25629530). Search the portal for the exact name.

ReleaseFull installer ISO
vCenter 9.1.0.0300VMware-VCSA-all-9.1.0.0300.25629530.iso
vCenter 9.1.0.0200VMware-VCSA-all-9.1.0.0200.25573614.iso
vCenter 9.0 GAVMware-VCSA-all-9.0.0.0.24755230.iso
vCenter 8.0 U3gVMware-VCSA-all-8.0.3-24853646.iso
vCenter 8.0 U3eVMware-VCSA-all-8.0.3-24674346.iso
vCenter 8.0 U3dVMware-VCSA-all-8.0.3-24322831.iso
vCenter 8.0 U3bVMware-VCSA-all-8.0.3-24262322.iso
vCenter 8.0 U3VMware-VCSA-all-8.0.3-24022515.iso
vCenter 8.0 U2cVMware-VCSA-all-8.0.2-23504390.iso
vCenter 8.0 U2aVMware-VCSA-all-8.0.2-22617221.iso
vCenter 8.0 U2VMware-VCSA-all-8.0.2-22385739.iso
vCenter 8.0 U1bVMware-VCSA-all-8.0.1-21860503.iso
vCenter 8.0 GAVMware-VCSA-all-8.0.0-20519528.iso

Before you upgrade vCenter

Install a vCenter patch ISO

  1. Upload the …-patch-FP.iso to a datastore and attach it to the vCenter appliance VM as a CD-ROM (connected).
  2. Open the VAMI at https://<vcenter>:5480, go to Update, choose Check Updates > Check CD ROM, run the pre-update checks, then stage and install.
  3. Or from the appliance shell: software-packages stage --iso, then software-packages install --staged (or software-packages install --iso in one step).

Further reading

The MOB is disabled – How to Enable the Managed Object Browser in vSphere 9

“The MOB is disabled” in vSphere 9? Enable the vCenter Managed Object Browser via enableDebugBrowse in vpxd.cfg, then disable it again after use.

Short answer: in vSphere 9 the vCenter Managed Object Browser (MOB, https://<vcenter>/mob) is disabled by default. To enable it, add <enableDebugBrowse>true</enableDebugBrowse> inside the <vpxd> block of /etc/vmware-vpx/vpxd.cfg and restart vmware-vpxd. Set it back to false when you’re done.

The MOB is a web interface for browsing the vSphere API object model: managed objects, their properties and methods. It’s handy for debugging, for looking up managed object IDs, or for checking which extension manages a VM (for example the vCLS VMs, see vCLS Retreat Mode).

When you try to access the Managed Object Browser (MOB) on your vCenter Server, you might be greeted with a screen like this:


“The MOB is disabled — The Managed Object Browser on this server is currently disabled. Please, contact your Virtual Infrastructure Administrator to enable it.”

Starting with vSphere 9, the MOB is disabled by default for security reasons. If you need to enable it (for example, for debugging or advanced troubleshooting), you can do so by editing the vpxd.cfg configuration file.

Below are the steps to enable the MOB safely:


✅ How to Enable MOB in vSphere 9

1️⃣ Take a backup of the configuration file

cp /etc/vmware-vpx/vpxd.cfg /var/core/vpxd.cfg

2️⃣ Open the config file in a text editor

vi /etc/vmware-vpx/vpxd.cfg

3️⃣ Add or update the entry
Inside the <vpxd> block, add:

<enableDebugBrowse>true</enableDebugBrowse>

For example:

<vpxd>
...
...
<enableDebugBrowse>true</enableDebugBrowse>
...
...
</vpxd>

4️⃣ Restart the vpxd service

service-control --restart vmware-vpxd

📚 Reference

For more information, see the official KB: How to disable access to the Managed Object Browser


✅ Tip: Remember to disable the MOB again after use to follow security best practices.

How to disable the MOB again

Change the entry in /etc/vmware-vpx/vpxd.cfg to <enableDebugBrowse>false</enableDebugBrowse> and restart the service with service-control --restart vmware-vpxd. The same setting disables the MOB on vCenter 7.x and 8.x (KB 320012).

lsdoctor: Check and Repair the vCenter Lookup Service (6.7 to 9.x)

Broadcom lsdoctor for vCenter 6.7-9.x: where to download it (KB 320837), how to run it safely, and which option fixes which Lookup Service problem.

lsdoctor (Lookup Service Doctor, lsdoctor.py) is Broadcom’s script for checking and repairing the vCenter Lookup Service: stale registrations, SSL trust mismatches, solution users and broken service registrations. The current build is lsdoctor-260716 (July 2026) and it supports vCenter 6.7 and later, including 7.x, 8.x and 9.x. Download it only from Broadcom KB 320837, take offline snapshots of every node in the SSO domain, and always start with the read-only --lscheck.

If the problem is an expired or mismatched certificate rather than the Lookup Service itself, check and replace certificates with vCert first.

lsdoctor at a glance

Current buildlsdoctor-260716.zip, added 16 Jul 2026 (always take the latest attachment from KB 320837)
SupportedvCenter Server 6.7 and later, VCSA or Windows-based, including 7.x, 8.x and 9.x. Support for the newest builds can lag behind a vCenter release.
DownloadOnly from Broadcom KB 320837. Verify the SHA256 listed in the KB.
Where to run itMost options run on any node in the same SSO site as the affected node. --stalefix and --solutionusers run on the affected node itself.
OutputFindings per node, shown as SSO site plus hostname/PNID, and the path to a JSON report
Safe first step--lscheck makes no changes

Before you run lsdoctor

  • Take offline snapshots of the whole SSO domain. KB 320837 is explicit: shut down all vCenter Servers and PSCs in the SSO domain at the same time, snapshot them, then power them on again. If you need to roll back, shut them all down and revert them together, otherwise replication between nodes breaks.
  • Pick the right node. Run checks from a node in the same SSO site as the one with the problem. For --stalefix and --solutionusers, log in to the affected node.
  • Check for a custom login banner. lsdoctor reads the vCenter version from /etc/issue. A custom banner makes it fail with IndexError: list index out of range (see fixing lsdoctor’s IndexError on 8.0.3).
  • Plan for follow-up work. Every option except --lscheck ends with a service restart, and most require re-registering external solutions such as backup, storage or monitoring plugins.

Download and install lsdoctor

Download the zip from KB 320837 and copy it to the node, for example with WinSCP. If WinSCP can’t connect to the appliance, set root’s login shell to bash first (chsh -s /bin/bash root). On the VCSA:

# cd /root
# sha256sum lsdoctor-260716.zip      # compare with the SHA256 in KB 320837
# unzip lsdoctor-260716.zip
# cd lsdoctor-*
# python lsdoctor.py --help

Always run lsdoctor from the extracted directory. On a Windows-based vCenter 6.7, extract the zip with Extract All, then run it with the bundled Python:

cd "C:\Program Files\VMware\vCenter Server\python"
.\python.exe <path_to_lsdoctor.py> <option>

lsdoctor options

OptionWhat it doesRun onFollow-up
-l, --lscheckChecks for common Lookup Service issues. Makes no changes.Any node in the SSO siteReview the output and the JSON report; it tells you which fix applies
-t, --trustfixCorrects SSL trust mismatches in the Lookup ServiceAny node in the SSO siteRestart services on all nodes in the SSO site; re-register external solutions
-s, --stalefixCleans up stale configuration left over from systems upgraded from 5.xThe affected nodeRestart all services; re-register external solutions
-u, --solutionusersRecreates the solution users for a nodeThe affected nodeRestart services on that node
-r, --rebuildRebuilds one or all service registrations for a nodeAny node in the SSO siteRestart services; re-register external solutions
-p, --pscHaUnconfigureRemoves a PSC High Availability (load balancer) configurationSee KB 320837Restart services on all PSCs; repoint vCenter; re-register external solutions

--rebuild uses registration templates that match your vCenter build. If lsdoctor has no template for your exact build, it asks you to pick the closest one. It also keeps automatic backups of the registrations it changes, and the same menu can restore them.

Which lsdoctor option for which problem

What you seeStart withThen
Upgrade, patch or repoint pre-checks fail with Lookup Service or registration errors--lscheckThe fix it recommends (usually --trustfix, --stalefix or --rebuild)
Plugins or solutions fail after replacing the Machine SSL certificate; certificate mismatch in Lookup Service registrations--lscheck--trustfix, or vCert option 4 (Manage SSL trust anchors)
Leftover registrations from a vCenter upgraded from 5.x--lscheck--stalefix on the affected node
Solution user errors on one node--lscheck--solutionusers on that node
Missing or broken service registrations--lscheck--rebuild
Retiring a PSC HA load balancer–--pscHaUnconfigure, then repoint vCenter
lsdoctor itself fails with IndexError: list index out of rangeCheck /etc/issueRestore the default banner temporarily

lsdoctor vs vCert

ToolFixesUse it when
lsdoctorLookup Service data: registrations, trust in registrations, solution users, stale entriesServices can’t find or trust each other, or upgrades fail on registration checks
vCertThe certificates themselves: Machine SSL, Solution Users, STS, VMCA, ESXi, trust anchorsCertificates are expired, expiring or replaced, or you see no healthy upstream after an expiry

The two overlap on trust anchors. A common sequence is: fix the certificates with vCert, then run lsdoctor --lscheck to confirm the Lookup Service registrations trust the new certificate.

Related vCenter guides

Full reference: Broadcom KB 320837 – Using the lsdoctor tool.

Critical Security Alert: Update to Fixed Version 8.0 U3d Immediately

CVE-2024-38812 is a CVSS 9.8 vCenter RCE exploited in the wild. Versions before 8.0 U3d and 7.0 U3t are affected: patch steps with software-packages.

Urgent Notice from VMware by Broadcom

Short answer: CVE-2024-38812 (CVSS 9.8, a heap overflow in vCenter’s DCERPC implementation) and CVE-2024-38813 are covered by VMSA-2024-0019. All vCenter versions before 8.0 U3d and 7.0 U3t are affected, the September 2024 patches were incomplete, and Broadcom confirmed exploitation in the wild in November 2024. If you are still below those builds, patch now, and always take the latest build from the advisory’s Response Matrix.

VMware has announced that the security patches released on September 17, 2024, intended to address CVE-2024-38812, did not fully mitigate the vulnerability. As a result, all customers are strongly advised to update to the latest version, 8.0 U3d, immediately. Patches for the 8.0 U2 line are also available to address this issue.

This urgent advisory applies to all vCenter Server users, as the newly identified vulnerabilities pose a significant security risk. Notably, two critical vulnerabilities were reported in vCenter Server, including a heap-overflow vulnerability and a privilege escalation vulnerability. These have been responsibly reported to VMware, which has now provided updates to address them.

Key Vulnerability: Heap-Overflow in vCenter Server (CVE-2024-38812)

Vulnerability Description:

A critical heap-overflow vulnerability was discovered in vCenter Server, specifically in its implementation of the DCERPC protocol. The issue has been assigned CVE-2024-38812 and carries a CVSSv3 base score of 9.8, placing it in the Critical severity range.

Known Attack Vectors:

This vulnerability can be exploited by a malicious actor who has network access to the vCenter Server. By sending a specially crafted network packet, the attacker could trigger the heap-overflow, potentially leading to remote code execution (RCE) on the affected system.

Why You Should Patch Now

This vulnerability could allow attackers to gain control over your vCenter Server environment, putting your infrastructure at risk for unauthorized access, data breaches, or service disruptions. Given the widespread use of vCenter Server for managing virtual environments, this threat is extremely serious, especially for businesses relying on VMware for critical operations.

Patch Availability

The new patches, which can be found in the Response Matrix, have been made available for both the 8.0 U3, 8.0 U2 and 7.0 U3 versions of vCenter Server. Customers should apply the new patches immediately to ensure their systems are protected.

What to Do:

  1. Check your version: Identify if your vCenter Server version is affected.
  2. Apply the patches: Use the Response Matrix provided by VMware to download and install the necessary updates.
  3. Follow VMware’s best practices: Regularly update your systems, review security advisories, and apply patches as soon as they are released to minimize security risks.

Mount VMware-vCenter-Server-Appliance-8.0.3.00400-24322831-patch-FP.iso to VCSA VM. Log in to the appliance shell as a user with super administrative privileges (for example, root) and run the following commands:

# To stage the ISO:
software-packages stage --iso

# To see the staged content:
software-packages list --staged

# To install the staged rpms:
software-packages install --staged

vCenter 8 Session Timeout Settings and the 8.0 U3b vSphere Client Idle Session Bug (Fixed in 8.0 U3c)

How to set the vSphere Client session timeout in vCenter 8.0 and 9.x, and why sessions broke after 50 idle minutes on 8.0 U3b until the 8.0 U3c fix.

Short answer: In vCenter 8.0, the vSphere Client session timeout is set in Administration > Deployment > Client Configuration > Edit > Session timeout (minutes, default 120). Alternatively, set session.timeout in /etc/vmware/vsphere-ui/webclient.properties. If sessions die after about 50 idle minutes on vCenter 8.0 U3b (8.0.3.00200), that is a Tomcat bug, not a setting. It is fixed in 8.0 U3c (build 24305161) and later.

vCenter 8 session timeout settings (vSphere Client)

By default, vSphere Client sessions close after 120 minutes of inactivity. You need the Global > Settings privilege to change it.

  1. In the vSphere Client Home menu, select Administration.
  2. Under Deployment, click Client Configuration.
  3. Click Edit. The Edit client configuration dialog opens.
  4. Enter the new value in minutes in Session timeout and click Save.
  5. Log in to the vSphere Client again for the change to take effect.

Alternative: webclient.properties

The same value lives in the vSphere Client properties file on the appliance. The file method is documented for vSphere 7.0 and 9.1:

# /etc/vmware/vsphere-ui/webclient.properties
session.timeout = 60

# apply
service-control --restart vsphere-ui

Uncomment the line if needed. The value is in minutes. The documentation says that a negative value or 0 means the client never times out. That is convenient in a lab but a bad idea in production. The vSphere Security guide recommends setting timeouts so that idle sessions cannot be misused.

vCenter 9 session timeout

The vSphere 9.1 documentation keeps both methods: Home > Administration > Deployment > Client Configuration > Edit, or session.timeout in /etc/vmware/vsphere-ui/webclient.properties. Default is still 120 minutes. After the change, restart the VMware vSphere Client service. Use service-control --restart vsphere-ui over SSH, or VAMI (https://<vcenter>:5480) > Services > VMware vSphere Client > Restart.

VersionUI pathFileApply
vCenter 8.0Administration > Deployment > Client Configurationwebclient.properties (session.timeout)Re-login (UI); restart vsphere-ui (file)
vCenter 9.xAdministration > Deployment > Client Configuration/etc/vmware/vsphere-ui/webclient.propertiesRestart VMware vSphere Client service

What went wrong in vCenter 8.0 U3b (8.0.3.00200)

vCenter Server 8.0 Update 3b (17 Sep 2024, build 24262322, patch VMware-vCenter-Server-Appliance-8.0.3.00200-24262322-patch-FP.iso) upgraded Apache Tomcat to 9.0.91. That Tomcat version changed the default of org.apache.catalina.connector.RECYCLE_FACADES from FALSE to TRUE. As a result, a vSphere Client session left idle for more than 50 minutes became invalid (PR 3439359). You could not log in or out, or use the client in that browser, until you cleared all cookies.

Symptoms listed in Broadcom KB 377734, usually after 1 to 2 idle hours:

  • The loading circle keeps spinning, and session timeouts occur.
  • Inventory errors: You have no privileges to view this object or it is deleted.
  • The login button is greyed out, or login fails with An error occurred while fetching identity providers.
  • ServiceClosedException: AsyncTokenProvider has been closed in /var/log/vmware/vsphere-ui/vsphere_client_virgo.log and /var/log/vmware/apig/apigw.log.

Raising the session timeout does not help here. The session breaks because of the Tomcat change, not because the configured timeout expires.

The fix: vCenter 8.0 U3c or later

vCenter Server 8.0 Update 3c (09 Oct 2024, ISO build 24305161, patch VMware-vCenter-Server-Appliance-8.0.3.00300-24305161-patch-FP.iso) contains only this fix (PR 3439359). Any later 8.0 U3 patch also includes it. Download the patch from the Broadcom Support Portal; this requires a login with an entitled account. If you patch now, go straight to the latest 8.0 U3 build rather than to U3c.

Workaround for 8.0 U3b (KB 377734)

If you cannot patch yet, disable RECYCLE_FACADES for the vSphere Client. SSH to vCenter as root:

root@vcsa-home [ ~ ]# cp /usr/lib/vmware-vsphere-ui/server/conf/catalina.properties /root/catalina.properties.bak

root@vcsa-home [ ~ ]# echo "org.apache.catalina.connector.RECYCLE_FACADES=false" >> /usr/lib/vmware-vsphere-ui/server/conf/catalina.properties

root@vcsa-home [ ~ ]# service-control --restart vsphere-ui

I ran exactly this on my home lab vCenter before 8.0 U3c was out. It only restarts the vSphere Client service.

Same symptoms on a newer build?

KB 377734 says that if you see this behaviour on a later version, you should hide third-party client plug-ins to find the cause. Go to Administration > Solutions > Client Plugins, select the third-party plug-in and click HIDE. This removes the plug-in’s UI extensions while its service keeps running.

Sources

Related on vdan.cz

vSphere Client Instability After vCenter 8.0.3.00200 (8.0 U3b): Moved

This note moved. The full article covers the vCenter 8.0 U3b idle session bug, KB 377734, the 8.0 U3c fix and vCenter session timeout settings.

This note has been merged into a single, updated article.

After upgrading to vCenter Server 8.0.3.00200 (8.0 Update 3b), the vSphere Client could become unresponsive after a long idle period. The cause was a changed Tomcat default (RECYCLE_FACADES), described in Broadcom KB 377734. It is fixed in vCenter 8.0 Update 3c and later.

The full article covers the symptoms, the KB workaround, the fixed builds and how to set the vSphere Client session timeout in vCenter 8.0 and 9.x:

vCenter 8 Session Timeout Settings and the 8.0 U3b vSphere Client Idle Session Bug (Fixed in 8.0 U3c)

VMSA-2024-0019: Critical VMware vCenter Server Vulnerabilities (CVE-2024-38812, CVE-2024-38813) Addressed

VMSA-2024-0019 covers vCenter heap-overflow CVE-2024-38812 and privilege escalation CVE-2024-38813. Affected versions and fixed builds (8.0 U3d, 7.0 U3t).

VMware has released an important security advisory, VMSA-2024-0019, detailing updates for VMware vCenter Server that address two significant vulnerabilities: a heap-overflow vulnerability (CVE-2024-38812) and a privilege escalation vulnerability (CVE-2024-38813). Both of these vulnerabilities could have severe implications if exploited, making it crucial for administrators to apply the necessary patches promptly.

Heap-Overflow Vulnerability (CVE-2024-38812)

Description: The first vulnerability, identified as CVE-2024-38812, is a heap-overflow vulnerability found in the vCenter Server’s implementation of the DCERPC protocol. This issue has been classified by VMware as Critical, with a maximum CVSSv3 base score of 9.8, indicating the potential for severe impact.

Known Attack Vectors: A malicious actor with network access to the vCenter Server can exploit this vulnerability by sending a specially crafted network packet. Successful exploitation could lead to remote code execution (RCE), allowing the attacker to execute arbitrary code on the vCenter Server with potentially full system privileges. This level of access could be used to disrupt services, exfiltrate sensitive data, or further compromise the virtual environment.

Privilege Escalation Vulnerability (CVE-2024-38813)

Description: The second vulnerability, CVE-2024-38813, is a privilege escalation flaw within the vCenter Server. VMware has rated this issue as Important, with a CVSSv3 base score of 7.5. While not as severe as the heap-overflow vulnerability, it still poses a significant risk.

Known Attack Vectors: An attacker with network access to the vCenter Server can exploit this vulnerability by sending a specially crafted network packet. If successful, the attacker could escalate their privileges to root, gaining full administrative control over the vCenter Server. This level of access could enable the attacker to make unauthorized changes, access sensitive information, or disrupt the entire virtual infrastructure.

More info VMSA-2024-0019:VMware vCenter Server updates address heap-overflow and privilege escalation vulnerabilities (CVE-2024-38812, CVE-2024-38813)

Resolving Privilege Issues in vCenter Server 8.0U2

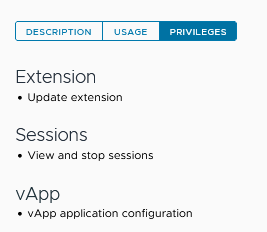
vCenter 8.0 U2 logs “Privilege check failed … missing permission Sessions.TerminateSession”? Add View and stop sessions to VsmSvcRole. No restart needed.

Short answer: after an upgrade to vCenter Server 8.0 U2, the Events tab can show “Privilege check failed for user VSPHERE.LOCAL\vmware-vsm-… for missing permission Sessions.TerminateSession”. The VsmSvcRole is missing the Sessions → View and stop sessions privilege. Add it under Administration → Roles and the warnings stop, with no service restart needed (KB 94967).

Introduction

Upgrading to the latest version of any software can sometimes introduce unexpected challenges. For administrators of VMware vCenter Server 8.0U2, one such issue is the appearance of privilege-related warnings in the vSphere Client. These warnings can cause concern but can be managed with the right steps.

Symptoms

After upgrading to vCenter Server 8.0U2, administrators may encounter the following warning in the vSphere Client’s Events tab: “Privilege check failed for user VSPHERE.LOCAL\vmware-vsm-… for missing permission Sessions.TerminateSession.”

This warning is flagged when the system checks the permissions associated with the VsmSvcRole role assigned to the solution user account.

Cause

The core of this issue lies in the permissions set for the VsmSvcRole. Despite having several default privileges, it lacks the “Sessions.TerminateSession” permission, which is crucial for certain administrative operations within the vSphere environment.

Immediate Workaround

Until VMware releases an update to address this issue, administrators can manually adjust the role permissions to prevent these warnings. Here’s how to implement this workaround:

  1. Log in to the vSphere Client with a user account that has administrative privileges.
  2. Navigate to Administration > Roles.
  3. Select the VsmSvcRole and click on EDIT.
  4. In the pop-up window, navigate to Sessions > View and stop sessions.
  5. Click SAVE to apply the changes. Ensure the role’s privileges now include the ability to terminate sessions.

This adjustment does not require any service restarts, making it a straightforward fix that can be implemented immediately.

Long-Term Resolution

VMware has acknowledged the issue and is working on a resolution to be included in a future software update. More info in Broadcom KB 94967; check it for the vCenter build that includes the fix.

vSphere 8.0 Update 2: Introducing Azure Active Directory Federated Authentication

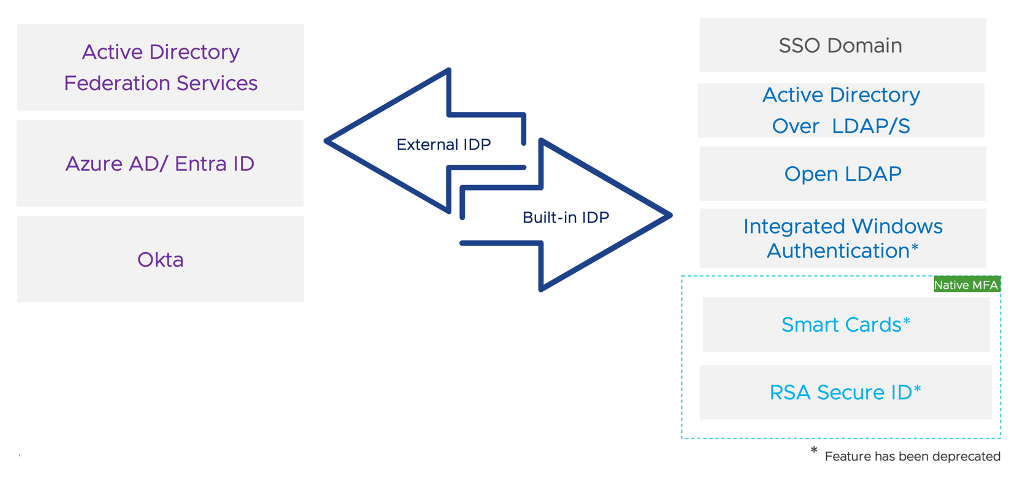
vSphere 8.0 Update 2 adds federated authentication with Azure Active Directory (Microsoft Entra ID) for vCenter, as presented at VMware Explore 2023.

At the 2023 VMware Explore event in Barcelona. I was on presentation with Viviana Miranda relates to the way users authenticate to vCenter.

vSphere 8.0 Update 2 update heralds a number of groundbreaking features, with one standout enhancement in user authentication methods for vCenter. vCenter Server 8.0 Update 2 has now incorporated federated authentication capabilities with Azure Active Directory.

Dive into the details of this integration and discover how to activate it.

The Advantages of External Identity Providers

Organizations that leverage external identity providers can expect to reap substantial benefits:

- Integration with existing identity provider infrastructure to streamline processes.
- Implementation of Single Sign-On to simplify access across services.
- Adherence to the best practices of role separation between infrastructure management and identity administration.
- Utilization of robust multi-factor authentication options that come with their chosen identity providers.

Supported Identity Providers in vSphere 8.0 U2

While our focus here is the Azure Active Directory integration, it’s essential to highlight the comprehensive range of authentication methods now supported with vCenter Server 8.0 U2.

More info: https://core.vmware.com/resource/vCenterAzureADFederation#Intro

💥VMware vCenter Server heap-overflow vulnerability – CVE-2023-20892, CVE-2023-20893, CVE-2023-20894, CVE-2023-20895, CVE-2023-20896

VMSA-2023-0014: multiple memory-corruption vulnerabilities in vCenter Server (CVE-2023-20892 to 20896, CVSS 5.9–8.1). Update as soon as possible.

Multiple memory corruption vulnerabilities in VMware vCenter Server were privately reported to VMware.

Please update ASAP – Risk: for network access to vCenter Server.

Advisory ID: VMSA-2023-0014
CVSSv3 Range: 5.9 - 8.1
Issue Date:2023-06-22
Response Matrix
ProductCVE IdentifierCVSS
v3
Fixed VerLinks
vCenter Server 8.0CVE-2023-20892 CVE-2023-20893 CVE-2023-20894 CVE-2023-208958.18.0 U1bNone
vCenter Server 8.0CVE-2023-208965.98.0 U1bNone
vCenter Server 7.0CVE-2023-20892 CVE-2023-20893 CVE-2023-20894 CVE-2023-208958.17.0 U3mNone
vCenter Server 7.0CVE-2023-208965.97.0 U3mNone
Cloud Foundation (vCenter Server) 5.xCVE-2023-20892 CVE-2023-20893 CVE-2023-20894 CVE-2023-208958.18.0 U1bKB88287
Cloud Foundation (vCenter Server) 5.xCVE-2023-208965.98.0 U1bKB88287
Cloud Foundation (vCenter Server) 4.xCVE-2023-20892 CVE-2023-20893 CVE-2023-20894 CVE-2023-208958.17.0 U3mKB88287
Cloud Foundation (vCenter Server) 4.xCVE-2023-208965.97.0 U3mKB88287

VMware vCenter Server heap-overflow vulnerability (CVE-2023-20892)

Description:
The vCenter Server contains a heap overflow vulnerability due to the usage of uninitialized memory in the implementation of the DCERPC protocol. VMware has evaluated the severity of this issue to be in the Important severity range with a maximum CVSSv3 base score of 8.1.

Known Attack Vectors:
A malicious actor with network access to vCenter Server may exploit this issue to execute arbitrary code on the underlying operating system that hosts vCenter Server.

VMware vCenter Server use-after-free vulnerability (CVE-2023-20893)

Description:
The vCenter Server contains a use-after-free vulnerability in the implementation of the DCERPC protocol. VMware has evaluated the severity of this issue to be in the Important severity range with a maximum CVSSv3 base score of 8.1.

Known Attack Vectors:
A malicious actor with network access to vCenter Server may exploit this issue to execute arbitrary code on the underlying operating system that hosts vCenter Server.

VMware vCenter Server out-of-bounds write vulnerability (CVE-2023-20894)

Description:
The vCenter Server contains an out-of-bounds write vulnerability in the implementation of the DCERPC protocol. VMware has evaluated the severity of this issue to be in the Important severity range with a maximum CVSSv3 base score of 8.1.

Known Attack Vectors:
A malicious actor with network access to vCenter Server may trigger an out-of-bound write by sending a specially crafted packet leading to memory corruption.

VMware vCenter Server out-of-bounds read vulnerability (CVE-2023-20895)

Description:
The vCenter Server contains a memory corruption vulnerability in the implementation of the DCERPC protocol. VMware has evaluated the severity of this issue to be in the Important severity range with a maximum CVSSv3 base score of 8.1

Known Attack Vectors:
A malicious actor with network access to vCenter Server may trigger a memory corruption vulnerability which may bypass authentication.

VMware vCenter Server out-of-bounds read vulnerability (CVE-2023-20896)

Description:
The vCenter Server contains an out-of-bounds read vulnerability in the implementation of the DCERPC protocol. VMware has evaluated the severity of this issue to be in the Moderate severity range with a maximum CVSSv3 base score of 5.9.

Known Attack Vectors:
A malicious actor with network access to vCenter Server may trigger an out-of-bounds read by sending a specially crafted packet leading to denial-of-service of certain services (vmcad, vmdird, and vmafdd).

Response Matrix