VMware Tanzu Community Edition now includes advanced software supply chain tooling that helps application teams deliver software more rapidly, securely, and efficiently at scale. The 0.11 release of Tanzu Community Edition, available today, introduces new supply chain choreography capabilities […]
Cisco bug CSCvz43359: with GENEVE offload on VIC 14xx, overlay traffic can leave the wrong vNIC. Symptoms and the fix in UCS Manager 4.2(1l).
According Release Notes for Cisco UCS Manager, Release 4.2(1l) We have a fix for CSCvz43359 Traffic using GENEVE overlay sometimes leaves wrong VNIC when GENEVE Offload is enabled on VIC14xx:
Defect ID
Symptom
First Bundle Affected
Resolved in Release
The following caveats related to NSX-T are resolved in Release 4.2(1l)
CSCvz43359
On a Cisco UCS server using an NSX-T topology, data traffic using a GENEVE overlay sometimes left the wrong vNIC when GENEVE Offload was enabled on a VIC 1400 series Fabric Interconnect. This issue is resolved.
4.2(1d)C
4.2(1l)C
Traffic using GENEVE overlay sometimes leaves wrong VNIC when GENEVE Offload is enabled on VIC14xx
Symptom: Rapid mac moves observed on Fabric Interconnect and northbound switches where mac address belongs to device using GENEVE overlay. pkcatp-uw in ESXi kernel was not able to observe this phenomenon. This was only observable via tcpdump on the physical VIC adapter in the debug shell.
Conditions: This was specifically seen in an NSX-T topology though more general use of GENEVE offloading in the hardware would likely show same behavior. The NSX-T TEP mac addresses should be ‘bound’ to a physical interface unless there is a topology change. In this circumstance, we observed the TEP macs rapidly moving from Fabric A to Fabric B and vice versa while the teaming/load balancing policy was set to Active/Active in ESXi and NSX. NSX-T uses BFD Control frames between hosts and BFD leverages GENEVE. When GENEVE Offloading is enabled in the VIC adapter policy, this causes some small number of these BFD frames to egress the wrong physical link which causes the unexpected mac move behavior on northbound devices.
ESXi PSOD “#PF Exception 14 in world xxxx:nsx-cfgagent” in NSX-T 3.1.3.x: how to identify it, cause, workaround and the fix in NSX-T 3.1.3.7 / VCF 4.4.1.
Short answer: “#PF Exception 14 in world xxxx:nsx-cfgagent” is a purple screen (PSOD) on ESXi hosts running NSX-T Data Center 3.1.3 or 3.1.3.x. In the message, xxxx stands for the world ID. It is triggered by bulk vMotions, which corrupt an internal data structure in the NSX distributed firewall. The fix is NSX-T 3.1.3.7 or later, or VCF 4.4.1 (NSX-T 3.1.3.7.4). The workaround is to set DRS to manual and avoid bulk vMotions. The original VMware KB 87352 is now Broadcom KB 318942.
What “xxxx:nsx-cfgagent” in the PSOD means
The KB title writes xxxx because the number changes on every crash. It is the ID of the ESXi world (thread) that was running when the host panicked. nsx-cfgagent is the NSX configuration agent on the host, and the frames in the backtrace belong to the NSX distributed firewall module (nsxt-vsip-<build>). A real panic message from the KB looks like this:
Panic Message: @BlueScreen: #PF Exception 14 in world 58524293:nsx-cfgagent IP 0x4180320430b3 addr 0x10
Back trace:
  0x451ac5c1b158:[0x4180320430b3]rn_walktree@(nsxt-vsip-19068435)#<None>+0x5b stack: 0x43261e082c18, ...
The KB also lists a second form of the same bug. There the world is a NetWorld-VM- thread, and the backtrace goes through the packet filter functions:
Panic Message: @BlueScreen: #PF Exception 14 in world 99566160:NetWorld-VM- IP 0x41801bf58a33 addr 0x0
... pfp_policy_lookup@(nsxt-vsip-18504670) ...
... pf_test_tcp@(nsxt-vsip-18504670) ...
... PFFilterPacket@(nsxt-vsip-18504670) ...
... VSIPDVFProcessPacketsInt@(nsxt-vsip-18504670) ...
#PF Exception 14 is a CPU page fault. It says nothing about the cause by itself; many different bugs produce one. What identifies this specific issue is the combination of three things:
the world name nsx-cfgagent (or NetWorld-VM-)
nsxt-vsip frames such as rn_walktree or pfp_policy_lookup in the backtrace
an NSX-T 3.1.3.x version on the host
How to confirm it in a PSOD screenshot or vmkernel.log
Read the first panic line. Take it from the purple screen (a screenshot from iLO, iDRAC or CIMC is enough). Look for #PF Exception 14 in world <number>:nsx-cfgagent.
Check the backtrace module. The frames should reference nsxt-vsip-<build>, for example rn_walktree, pfp_policy_lookup or PFFilterPacket.
Check vmkernel.log. After the host is back, look in /var/run/log/vmkernel.log around the vMotion import. The KB shows firewall state import messages like the ones below.
Check what was happening. Correlate with vCenter tasks. The crash follows a burst of vMotions, for example a DRS rebalance, maintenance mode or a host evacuation.
ImportStateTLV entry type 12, len 52, cnt 1
Importing from source version RELEASEbuild-19068435
pfr_unroute_kentry: delete failed.
pfp_add_table_one_addr: failed to add ke
rn_addmask: mask impossibly already in tree
pfp_add_addr_with_rule: failed
VSIPConversionCreateRuleSet: Cannot insert #1060 rule 26238: 22
pf_rollback_rules: rs_num: 1, anchor: mainrs
Affected versions and trigger scenarios
Item
Per Broadcom KB 318942
NSX version
NSX-T Data Center 3.1.3 and 3.1.3.x
ESXi
6.7, 7.x
VCF
4.x
Cause
Corruption in an internal data structure of the firewall code
Fixed in
NSX-T Data Center 3.1.3.7 and later; VCF 4.4.1 (NSX-T 3.1.3.7.4)
Workaround
Set DRS to manual on the cluster and avoid bulk vMotions
The KB lists these probable triggers during bulk vMotions:
Migrating many VMs that each have multiple vNICs.
Multiple IP sets in CIDR form per firewall rule.
Multiple rules that contain the same IP sets.
VMs moving from a host that has not been upgraded to a host that has been upgraded. This makes the upgrade window, when many hosts are evacuated, the riskiest time.
Fix: which NSX-T build to go to
When I first wrote this post in 2022, the guidance was to go to 3.1.3.6.1. The current Broadcom KB now says the issue is resolved in NSX-T Data Center 3.1.3.7 and later. It also still points to a separate problem in 3.1.3.6: KB 318290 (old 87627), where an Edge with an L4 load balancer stops passing traffic because of a datapath memory leak. That issue is also resolved in 3.1.3.7. In practice:
Standalone NSX-T 3.1.3.x: upgrade to 3.1.3.7 or later. Don’t stop at 3.1.3.6.
VCF 4.x: upgrade to VCF 4.4.1 (NSX-T 3.1.3.7.4). If you can’t, the KB tells you to open a Support Request before you patch NSX-T manually outside SDDC Manager.
Until you upgrade: set DRS to manual and move VMs in small batches.
Keep the support status in mind as well. Broadcom KB 421705 lists NSX 3.1.x End of Service as 7 April 2025. Any environment that still hits this PSOD is running an out-of-support NSX release, and the real fix is an upgrade to a supported NSX version.
Tweet Thank you to everyone who applied for vExpert and to the vExpert PROs for managing the voting process, it’s a lot of work! We are pleased to announce the list of 2022 vExperts. You can visit the vExpert Directory to see the list and profiles of each vExpert. All of the new and returning … Continued The post vExpert 2022 Awards Announcement appeared first on VMware vExpert Blog.
I am always on the lookout for new and interesting hardware platforms that can benefit the VMware Homelab Community. In the month of January, there were a number of new announcements that I had been following including news from the Computer Electronic Show (CES) but also a couple of product releases from vendors that I […]
Boot ESXi from a RAID 1 M.2 volume on Cisco UCS-M2-HWRAID: controller limits, UCS Manager, Intersight and CIMC steps, and ESXi 8/9 boot device rules.
Short answer: UCS-M2-HWRAID is Cisco’s boot-optimized M.2 RAID controller for UCS M5 and M6 servers. It holds two identical M.2 SATA SSDs and supports only RAID 1 or JBOD (default JBOD). It boots only in UEFI mode, and one virtual drive always uses the full capacity. To boot ESXi, create a RAID 1 LUN in UCS Manager, Intersight or CIMC, set a UEFI boot policy to local disk (MSTOR-RAID), and install ESXi to that volume.
What is UCS-M2-HWRAID
The Cisco Boot-Optimized M.2 RAID Controller (PID UCS-M2-HWRAID) is a module that plugs into the mini-storage connector on the motherboard. It has two slots for SATA M.2 SSDs and an integrated 6 Gbps SATA RAID controller. In UCS Manager, Intersight and CIMC the controller shows as MSTOR-RAID. Its job is to give ESXi a mirrored local boot device without using the front drive bays or an SD card.
Property
Value (Cisco documentation)
Servers
UCS C220 M5, C240 M5, C480 M5, B200 M5, B480 M5 (UCS Manager 4.1 guide); also required for M.2 SATA on C220 M6 (spec sheet)
Minimum firmware
UCS Manager 4.0(4a) for the RAID procedure (tech note); Cisco IMC / UCS Manager 4.2(1) on M6
M.2 drives
240 GB and 960 GB SATA M.2 (UCSM 4.1 guide); C220 M6 spec sheet lists UCS-M2-240G, UCS-M2-480G, UCS-M2-960G
RAID levels
RAID 1 or JBOD only (default JBOD)
Boot mode
UEFI only; legacy boot not supported
Virtual drives
One, using the entire disk capacity
Mixing drives
Not supported (use two identical SSDs)
Hot-plug
Not supported; power the server off to replace a drive (M6 spec sheet)
Other UCS Manager limitations: the Local Disk Configuration policy is not supported, the LUN must be created in the Local LUNs tab of a storage profile (not with controller definitions), and existing LUN migration is not supported.
UCS-M2-HWRAID in UCS Manager: create the RAID 1 boot LUN
These screenshots are from my UCS Manager setup.
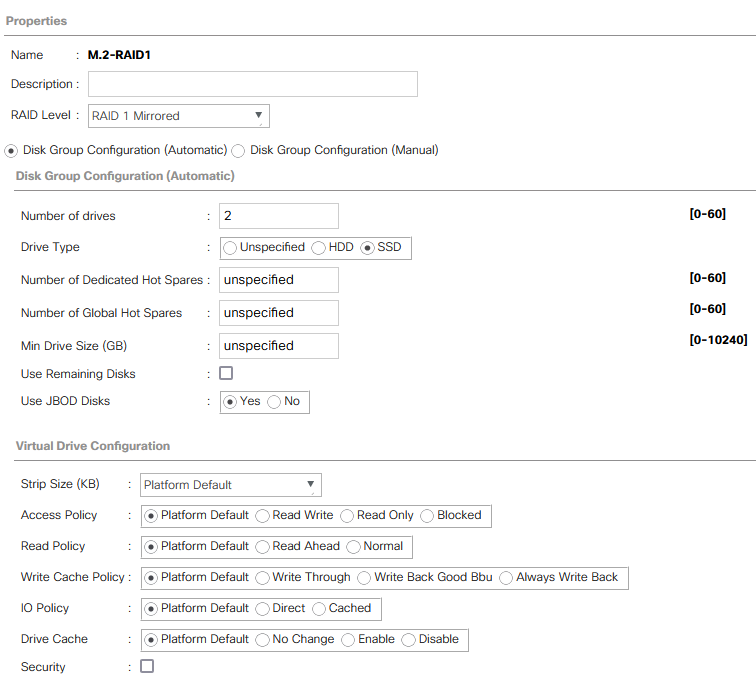
1. Disk group policy: Storage > Storage Policies > root > Disk Group Policies
Create a policy (here M.2-RAID1) with RAID Level RAID 1 Mirrored, 2 drives, drive type SSD.
If the service profile association fails with Server does not fulfill Local Disk config requirements, Cisco’s tech note says to use Disk Group Configuration (Manual) with the two M.2 slots and to disable pSATA. With manual configuration, leave the span ID unspecified and set the disk role to normal.
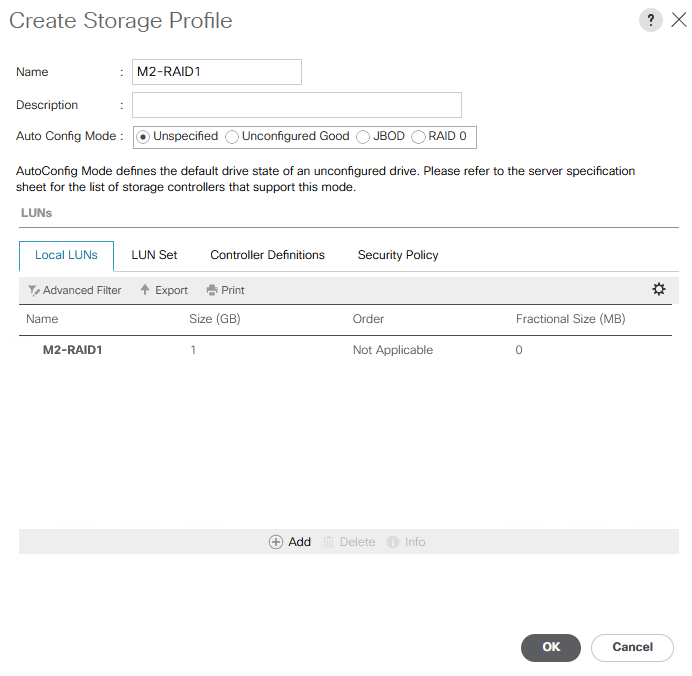
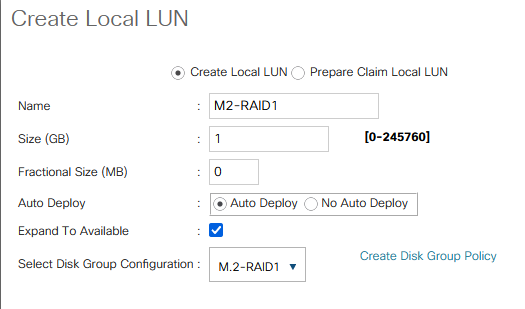
Add a local LUN, select the disk group policy and enable Expand To Available. The controller supports only one LUN over the whole mirror anyway.
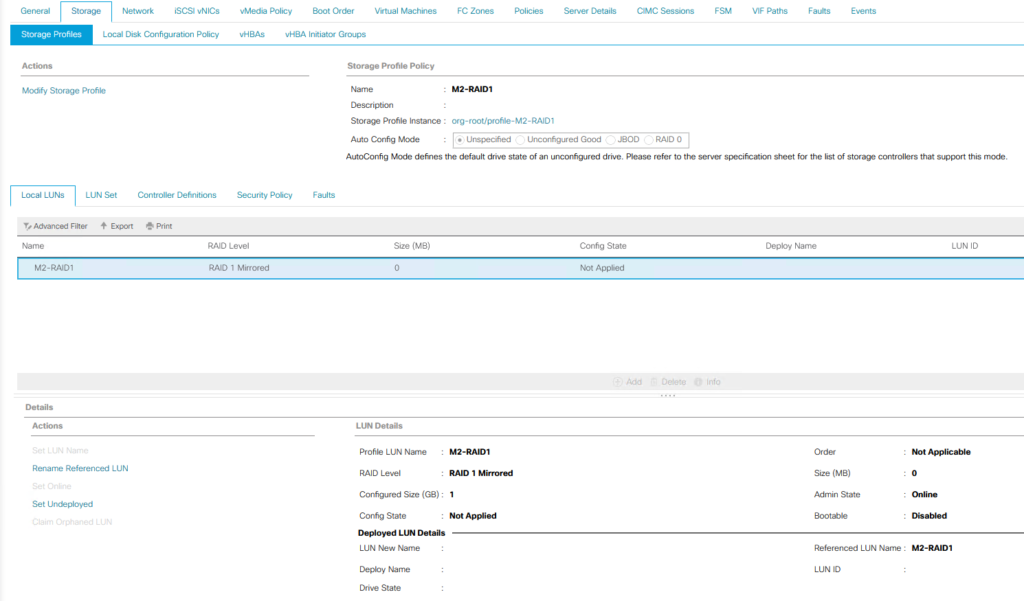
4. Attach the storage profile to the service profile
In the service profile, open Storage > Storage Profiles > Modify Storage Profile and select the profile. The LUN shows Not Applied until the profile is associated.
5. Boot policy: UEFI, Local Disk first
Use a boot policy with boot mode UEFI (the controller does not boot in legacy mode) and put the local disk first.
UCS-M2-HWRAID in Intersight Managed Mode
Create a Storage policy and enable M.2 RAID Configuration. Keep the default virtual drive name MStorBootVd or set your own. Select the M.2 controller slot: MSTOR-RAID-1 for C-Series and X-Series. Only the B200 M6 can have a second controller (MSTOR-RAID-2).
Create a Boot Order policy (Policies > Create Policy > UCS Server > Boot Order) in UEFI mode. Add Local Disk with the slot set to the M.2 controller from the server inventory (MSTOR-RAID), then add virtual media for the installer.
Add both policies to the server profile and deploy it. The RAID 1 volume should be visible in the ESXi installer.
UCS-M2-HWRAID in standalone CIMC
Storage > Cisco Boot optimized M.2 Raid controller (MSTOR-RAID). In Physical Drive Info, check that both drives are healthy.
Create Virtual Drive from Unused Physical Drives, move both M.2 drives to the drive group, choose RAID 1 (the only option on this controller) and click Create Virtual Drive.
Compute > Configure Boot Order > Advanced. Add Local HDD with slot MSTOR-RAID, or use Add Embedded Storage.
Without CIMC access, the same controller menu is in BIOS setup: press F2 during POST, then go to Advanced > Cisco Boot optimized M.2 RAID Controller.
UCS-M2-HWRAID ESXi driver and support
Cisco does not ship a separate ESXi driver download for this controller in the documents above. Whether a given ESXi release is supported on your server with this controller is defined by the Cisco UCS Hardware and Software Compatibility tool (ucshcltool.cloudapps.cisco.com) and the Broadcom Compatibility Guide. Check both for your exact server, firmware bundle and ESXi build before you upgrade. Install from the Cisco custom ESXi ISO so that the Cisco drivers match the firmware.
After installation, confirm which driver ESXi bound to the controller, and that the boot device is the RAID volume:
esxcli storage core adapter list
esxcli storage core device list
ESXi 7, 8 and 9 boot device requirements
Broadcom KB 317631 (formerly 85685, “SD card/USB boot device revised guidance”) is the reference for boot media. A RAID 1 M.2 SATA SSD volume is exactly the kind of local persistent boot device it recommends:
Requirement
ESXi 8.x
ESX 9.x
Boot device size
32 GB minimum, 128 GB recommended
128 GB minimum
Endurance
128 TBW over 5 years
IO performance
At least 100 MB/s
Media
PCIe NVMe, SAS, SATA/SATADOM SSD; industrial-grade flash (SLC or pSLC)
SD card / USB
Still supported through VCF 9.0 on previously certified servers, but not recommended; new platforms are not certified with SD/USB boot
Every M.2 size listed above (240, 480 or 960 GB) meets the ESX 9 minimum of 128 GB. Check the endurance rating of your specific SSD model against the 128 TBW requirement. On ESXi 7.x, SD cards can still hold all partitions, but Broadcom strongly recommends moving to a persistent device. If you are replacing SD cards on M5/M6 servers, UCS-M2-HWRAID is the natural choice.
Cisco UCS / Proactive HA Registration / vCenter server credentials / Register
Cisco UCS / Proactive HA Registration / Register
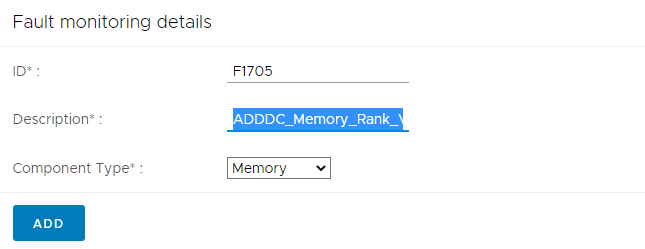
How Could I check it? Edit Proactive HA / Providers
It is better use Name “ADDDC_Memory_Rank_VLS” without spaces. On my picture I used “My F1705 Alerts”
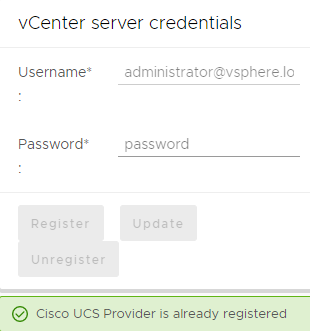
Adding Custom Alert is only possible with unregistered Cisco UCS Provider, it is better to do it immediatly after Cisco UCS Manager Plugin instalation.
Now I can deceided If I will block F1705 or NOT. I personaly preffer to have F1705 Alert under Proactive HA. Then I only restart Blades with F1705. During reboot Hard-PPRpermanently remaps accesses from a designated faulty row to a designated spare row.
The fastest workaround for Log4j CVE-2021-44228 (VMSA-2021-0028) on vCenter Server 7.0, 6.7 and 6.5, and why patching is the real fix.
https://logging.apache.org/log4j/2.x/
Apache Log4j open source component has security bug (CVE-2021-44228 – VMSA-2021-0028). It is neccesary to fix vCenter Server 7.0.x, vCenter 6.7.x & vCenter 6.5.x.
Connected to service

    * List APIs: "help api list"
    * List Plugins: "help pi list"
    * Launch BASH: "shell"

Command> shell
Shell access is granted to root
root@localhost [ ~ ]# cd /tmp
root@localhost [ /tmp ]# vim vc_log4j_mitigator.py
Run script python vc_log4j_mitigator.py
root@localhost [ /tmp ]# python vc_log4j_mitigator.py
2021-12-21T10:38:20 INFO main: Script version: 1.6.0
2021-12-21T10:38:20 INFO main: vCenter type: Version: 7.0.2.00500; Build: 18455184; Deployment type: embedded; Gateway: False; VCHA: False; Windows: False;
A service stop and start is required to complete this operation.  Continue?[y]y
2021-12-21T10:38:23 INFO stop: stopping services
2021-12-21T10:38:46 INFO process_jar: Found a VULNERABLE FILE: /opt/vmware/lib64/log4j-core-2.13.0.jar
2021-12-21T10:38:46 INFO backup_file: VULNERABLE FILE: /opt/vmware/lib64/log4j-core-2.13.0.jar backed up to /tmp/tmpxi89fco8/opt/vmware/lib64/log4j-core-2.13.0.jar.bak
2021-12-21T10:38:47 INFO process_jar: VULNERABLE FILE: /opt/vmware/lib64/log4j-core-2.13.0.jar backed up to /tmp/tmpxi89fco8/opt/vmware/lib64/log4j-core-2.13.0.jar.bak
2021-12-21T10:39:03 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.13.1.jar
2021-12-21T10:39:03 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:04 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:04 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.8.2.jar
2021-12-21T10:39:04 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.8.2.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.8.2.jar.bak
2021-12-21T10:39:04 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.8.2.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.8.2.jar.bak
2021-12-21T10:39:06 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.11.0.jar
2021-12-21T10:39:06 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.11.0.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.11.0.jar.bak
2021-12-21T10:39:06 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.11.0.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.11.0.jar.bak
2021-12-21T10:39:07 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.11.2.jar
2021-12-21T10:39:07 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.11.2.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.11.2.jar.bak
2021-12-21T10:39:07 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware/common-jars/log4j-core-2.11.2.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/common-jars/log4j-core-2.11.2.jar.bak
2021-12-21T10:39:08 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware/cis_upgrade_runner/payload/component-scripts/sso/lstool/lib/log4j-core-2.13.1.jar
2021-12-21T10:39:08 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware/cis_upgrade_runner/payload/component-scripts/sso/lstool/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/cis_upgrade_runner/payload/component-scripts/sso/lstool/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:08 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware/cis_upgrade_runner/payload/component-scripts/sso/lstool/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware/cis_upgrade_runner/payload/component-scripts/sso/lstool/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:14 INFO process_jar: Found a VULNERABLE FILE: /tmp/tmpn2a_0ql2/WEB-INF/lib/log4j-core-2.13.3.jar
2021-12-21T10:39:14 INFO backup_file: VULNERABLE FILE: /tmp/tmpn2a_0ql2/WEB-INF/lib/log4j-core-2.13.3.jar backed up to /tmp/tmpxi89fco8/tmp/tmpn2a_0ql2/WEB-INF/lib/log4j-core-2.13.3.jar.bak
2021-12-21T10:39:15 INFO process_war: Found a VULNERABLE WAR file with: /usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-fileupload.war
2021-12-21T10:39:15 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-fileupload.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-fileupload.war.bak
2021-12-21T10:39:15 INFO process_war: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-fileupload.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-fileupload.war.bak
2021-12-21T10:39:15 INFO process_jar: Found a VULNERABLE FILE: /tmp/tmpxn5_4ah_/WEB-INF/lib/log4j-core-2.13.3.jar
2021-12-21T10:39:15 INFO backup_file: VULNERABLE FILE: /tmp/tmpxn5_4ah_/WEB-INF/lib/log4j-core-2.13.3.jar backed up to /tmp/tmpxi89fco8/tmp/tmpxn5_4ah_/WEB-INF/lib/log4j-core-2.13.3.jar.bak
2021-12-21T10:39:16 INFO process_war: Found a VULNERABLE WAR file with: /usr/lib/vmware-updatemgr/bin/jetty/webapps/root.war
2021-12-21T10:39:16 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/webapps/root.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/webapps/root.war.bak
2021-12-21T10:39:16 INFO process_war: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/webapps/root.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/webapps/root.war.bak
2021-12-21T10:39:16 INFO process_jar: Found a VULNERABLE FILE: /tmp/tmpa4w275ot/WEB-INF/lib/log4j-core-2.13.3.jar
2021-12-21T10:39:16 INFO backup_file: VULNERABLE FILE: /tmp/tmpa4w275ot/WEB-INF/lib/log4j-core-2.13.3.jar backed up to /tmp/tmpxi89fco8/tmp/tmpa4w275ot/WEB-INF/lib/log4j-core-2.13.3.jar.bak
2021-12-21T10:39:17 INFO process_war: Found a VULNERABLE WAR file with: /usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-filedownload.war
2021-12-21T10:39:17 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-filedownload.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-filedownload.war.bak
2021-12-21T10:39:18 INFO process_war: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-filedownload.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-filedownload.war.bak
2021-12-21T10:39:21 INFO process_jar: Found a VULNERABLE FILE: /tmp/tmpxv_znca3/WEB-INF/lib/log4j-core-2.13.1.jar
2021-12-21T10:39:21 INFO backup_file: VULNERABLE FILE: /tmp/tmpxv_znca3/WEB-INF/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/tmp/tmpxv_znca3/WEB-INF/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:22 INFO process_war: Found a VULNERABLE WAR file with: /usr/lib/vmware-sso/vmware-sts/webapps/ROOT.war
2021-12-21T10:39:22 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-sso/vmware-sts/webapps/ROOT.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-sso/vmware-sts/webapps/ROOT.war.bak
2021-12-21T10:39:24 INFO process_war: VULNERABLE FILE: /usr/lib/vmware-sso/vmware-sts/webapps/ROOT.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-sso/vmware-sts/webapps/ROOT.war.bak
2021-12-21T10:39:25 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware-sso/vmware-sts/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar
2021-12-21T10:39:25 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-sso/vmware-sts/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware-sso/vmware-sts/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:26 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware-sso/vmware-sts/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware-sso/vmware-sts/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:28 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware-dbcc/lib/log4j-core-2.8.2.jar
2021-12-21T10:39:28 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-dbcc/lib/log4j-core-2.8.2.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware-dbcc/lib/log4j-core-2.8.2.jar.bak
2021-12-21T10:39:29 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware-dbcc/lib/log4j-core-2.8.2.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware-dbcc/lib/log4j-core-2.8.2.jar.bak
2021-12-21T10:39:32 INFO process_jar: Found a VULNERABLE FILE: /tmp/tmprq0yfnd1/WEB-INF/lib/log4j-core-2.13.1.jar
2021-12-21T10:39:32 INFO backup_file: VULNERABLE FILE: /tmp/tmprq0yfnd1/WEB-INF/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/tmp/tmprq0yfnd1/WEB-INF/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:33 INFO process_war: Found a VULNERABLE WAR file with: /usr/lib/vmware-lookupsvc/webapps/ROOT.war
2021-12-21T10:39:33 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-lookupsvc/webapps/ROOT.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-lookupsvc/webapps/ROOT.war.bak
2021-12-21T10:39:34 INFO process_war: VULNERABLE FILE: /usr/lib/vmware-lookupsvc/webapps/ROOT.war backed up to /tmp/tmpxi89fco8/usr/lib/vmware-lookupsvc/webapps/ROOT.war.bak
2021-12-21T10:39:34 INFO process_jar: Found a VULNERABLE FILE: /usr/lib/vmware-lookupsvc/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar
2021-12-21T10:39:35 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-lookupsvc/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware-lookupsvc/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:35 INFO process_jar: VULNERABLE FILE: /usr/lib/vmware-lookupsvc/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar backed up to /tmp/tmpxi89fco8/usr/lib/vmware-lookupsvc/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar.bak
2021-12-21T10:39:37 INFO _patch_file: Found VULNERABLE FILE: /usr/lib/vmware-vmon/java-wrapper-vmon
2021-12-21T10:39:37 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-vmon/java-wrapper-vmon backed up to /tmp/tmpxi89fco8/usr/lib/vmware-vmon/java-wrapper-vmon.bak
2021-12-21T10:39:37 INFO patch_vum: Found a VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/start.ini
2021-12-21T10:39:37 INFO backup_file: VULNERABLE FILE: /usr/lib/vmware-updatemgr/bin/jetty/start.ini backed up to /tmp/tmpxi89fco8/usr/lib/vmware-updatemgr/bin/jetty/start.ini.bak
2021-12-21T10:39:37 INFO print_summary:
=====     Summary     =====
Backup Directory: /tmp/tmpxi89fco8
List of processed java archive files:

/opt/vmware/lib64/log4j-core-2.13.0.jar
/usr/lib/vmware/common-jars/log4j-core-2.13.1.jar
/usr/lib/vmware/common-jars/log4j-core-2.8.2.jar
/usr/lib/vmware/common-jars/log4j-core-2.11.0.jar
/usr/lib/vmware/common-jars/log4j-core-2.11.2.jar
/usr/lib/vmware/cis_upgrade_runner/payload/component-scripts/sso/lstool/lib/log4j-core-2.13.1.jar
/usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-fileupload.war
/usr/lib/vmware-updatemgr/bin/jetty/webapps/root.war
/usr/lib/vmware-updatemgr/bin/jetty/webapps/vum-filedownload.war
/usr/lib/vmware-sso/vmware-sts/webapps/ROOT.war
/usr/lib/vmware-sso/vmware-sts/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar
/usr/lib/vmware-dbcc/lib/log4j-core-2.8.2.jar
/usr/lib/vmware-lookupsvc/webapps/ROOT.war
/usr/lib/vmware-lookupsvc/webapps/ROOT/WEB-INF/lib/log4j-core-2.13.1.jar

List of processed configuration files:

/usr/lib/vmware-vmon/java-wrapper-vmon
/usr/lib/vmware-updatemgr/bin/jetty/start.ini

Total fixed: 16

    NOTE: Running this script again with the --dryrun
    flag should now yield 0 vulnerable files.

Log file: /var/log/vmsa-2021-0028_2021_12_21_10_38_20.log
===========================
2021-12-21T10:39:37 INFO start: starting services
2021-12-21T10:52:47 INFO main: Done.
Verify python vc_log4j_mitigator.py -r
root@localhost [ /tmp ]# python vc_log4j_mitigator.py -r
2021-12-21T11:10:01 INFO main: Script version: 1.6.0
2021-12-21T11:10:01 INFO main: vCenter type: Version: 7.0.2.00500; Build: 18455184; Deployment type: embedded; Gateway: False; VCHA: False; Windows: False;
2021-12-21T11:10:01 INFO main: Running in dryrun mode.
2021-12-21T11:11:01 INFO print_summary:
=====     Summary     =====

No vulnerable files found!

Total found: 0
Log file: /var/log/vmsa-2021-0028_2021_12_21_11_10_01.log
===========================
2021-12-21T11:11:01 INFO main: Done.
vc_log4j_mitigator.py [-h] – helps and more options
root@localhost [ /tmp ]# python vc_log4j_mitigator.py -h
usage: vc_log4j_mitigator.py [-h] [-d dirnames [dirnames ...]] [-a] [-r] [-b BACKUP_DIR] [-l LOG_DIR]

VMSA-2021-0028 vCenter tool; Version: 1.6.0 This tool deletes the JndiLookup.class file from *.jar and *.war files. On Windows systems the tool will by default traverse the folders identified by the VMWARE_CIS_HOME, VMWARE_CFG_DIR, VMWARE_DATA_DIR and VMWARE_RUNTIME_DATA_DIR
variables. On vCenter Appliances the tool will search by default from the root of the filesystem. All modified files are backed up if the process needs to be reversed due to an error.

optional arguments:
  -h, --help            show this help message and exit
  -d dirnames [dirnames ...], --directories dirnames [dirnames ...]
                        space separated list of directories to check recursively for CVE-2021-44228 vulnerable java archive files.
  -a, --accept-services-restart
                        accept the restart of the services without having manual prompt confirmation for the same
  -r, --dryrun          Run the script and log vulnerable files without mitigating them. The vCenter services are not restarted with this option.
  -b BACKUP_DIR, --backup-dir BACKUP_DIR
                        Specify a backup directory to store original files.
  -l LOG_DIR, --log-dir LOG_DIR
                        Specify a directory to store log files.
On the 1st day of #12DaysOfK8s, let’s get started with the basics: What is Kubernetes? ☸️ Find out in 5 minutes or less by watching this lightboard video with @vstegeler. More to come tomorrow!
NSX Edge design on Cisco UCS for NSX 4.x and VCF 9: Edge VM vs bare metal, vNIC pairs without fabric failover, TEP MTU and VIC Geneve offload.
Short answer: On Cisco UCS, NSX Edge VMs usually go on a small, dedicated ESX edge cluster. Give each Edge a pair of vNICs, one pinned to Fabric A and one to Fabric B, with UCS fabric failover disabled. Redundancy then comes from the Edge’s fp-eth active/standby mapping, not from the Fabric Interconnect. Keep TEP MTU consistent: 1700 or more, ideally 9000 end to end. Enable Geneve offload in the VIC adapter policy for the host transport nodes. For VCF 9, follow the VCF Edge Cluster design library.
I wrote this in 2021 for NSX-T 3.x, because Cisco’s design guides did not cover Edge placement. This September 2026 refresh covers NSX 4.2 and VCF 9.0/9.1, checked against Broadcom TechDocs and Cisco documentation. Parts that apply only to the 2021 design are labelled.
Where is the NSX-T design guide now?
Version
Design reference
NSX-T 3.x (2021, this post’s original basis)
VMware NSX-T Reference Design Guide. The old communities.vmware.com links no longer work.
From vCenter / NSX. Passwords managed by VCF Operations.
Installed from ISO or PXE, then registered manually with NSX Manager
Data path interfaces
4 datapath vNICs
Up to 16 physical interfaces
Strengths
Easy to scale up, vSphere HA recovery, enough performance for most cases
Better small-packet performance, can use several 100G links
UCS specifics
Runs on any UCS ESX host. Uses VIC vNICs through the VDS.
The VCF 9.0 NIC list includes Cisco VIC 1300 and 1400 series (VIC 15000 is not listed). You must configure enough RX/TX queues in UCS Manager for one queue per datapath core. The CPU needs AES-NI and 1 GB huge pages.
Edge VM sizes (VCF 9.0 docs): Small 2 vCPU / 4 GB (proof of concept only), Medium 4 vCPU / 8 GB (L2 to L4 under 2 Gbps), Large 8 vCPU / 32 GB (2 to 10 Gbps, L7 load balancing, TLS inspection), Extra Large 16 vCPU / 64 GB (VPN, IDS/IPS, URL filtering, malware prevention). All sizes use a 200 GB disk.
NSX Edge design on Cisco UCS: uplinks and TEPs on vNICs
The VCF 9.1 edge cluster design recommends a dedicated vSphere cluster for Edges. It limits Edges per host to the number of available physical NICs and gives each Edge its own pair of pNICs. fp-eth0 maps to pNIC 1 active / pNIC 2 standby, and fp-eth1 maps to pNIC 2 active / pNIC 1 standby. Each Edge peers BGP only with the ToRs in its own rack, with BFD. On an FI-attached UCS server, “pNIC 1 / pNIC 2” means a Fabric A vNIC and a Fabric B vNIC:
Create a vNIC pair per Edge (for example edge1-A on Fabric A and edge1-B on Fabric B), plus separate vNICs for host management, vMotion and storage.
Disable fabric failover on these vNICs. Cisco’s teaming guidance for FI-attached servers says to use either fabric failover or OS/vSwitch teaming, never both. The VDS/Edge active/standby mapping is the teaming here.
On the VDS, use two trunk port groups: one with the Fabric A uplink active and Fabric B standby, and one with the reverse. Connect fp-eth0 and fp-eth1 to them. Cisco supports only “Route based on originating port ID” and “source MAC hash” on FI-attached VICs. IP hash is not supported.
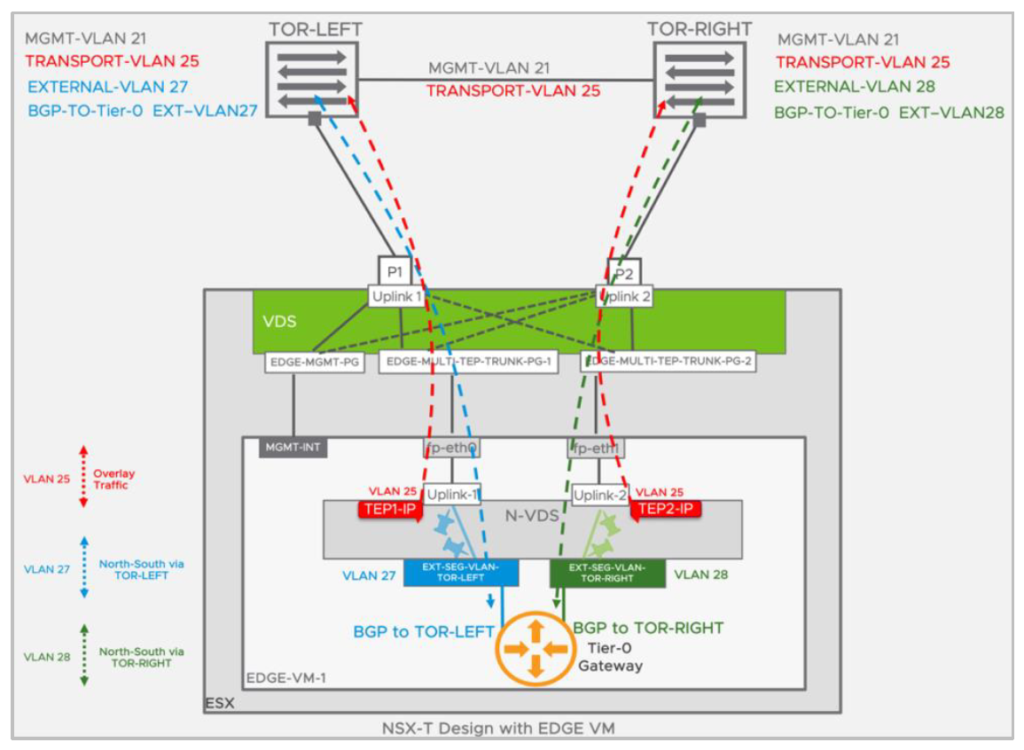
In the Edge uplink profile, use two TEPs (multi-TEP) and add named teaming policies that pin each Tier-0 uplink VLAN to one uplink. The Fabric Interconnects run in end-host mode, so the BGP peers are the upstream switches, not the FIs.
NSX-T 3.0 single N-VDS multi-TEP Edge VM design (source: VMware NSX-T 3.0 Edge Design Step-by-Step). The topology is still valid in NSX 4.x and VCF 9.
The 2021 named teaming example still applies: two policies, PIN-TO-TOR-LEFT (“uplink-1” active) and PIN-TO-TOR-RIGHT (“uplink-2” active), one per external VLAN segment. On UCS, left and right become Fabric A and Fabric B.
MTU for NSX on UCS
NSX requires an MTU of at least 1600 bytes and recommends 1700 to allow for Geneve header growth. For better throughput, set the global TEP MTU, uplink profile MTU and VDS MTU to 9000 when the underlay supports jumbo frames. VCF also requires the Edge TEP MTU to match the host TEP MTU in the same overlay transport zone. On UCS, set the vNIC MTU to 9000, as Cisco’s VIC best practices recommend. The QoS system class and the upstream switches must also carry jumbo frames. Guest VMs can use up to 8800 on a 9000 underlay.
VIC adapter policy and Geneve offload
Supported on VIC 1400 from UCSM/IMC 4.1(2) (NSX standard mode) and 4.1(3) (Enhanced Datapath, nenic-ens driver). Supported on VIC 15000 from 4.2(3). Not supported on VIC 1200/1300. Geneve offload is disabled by default.
Recommended Ethernet adapter policy with Geneve offload (UCSM 4.3 guide): TX queues 1, TX ring 4096, RX queues 8, RX ring 4096, completion queues 16, interrupts 32, RSS on, GENEVE offload enabled. RoCEv2 cannot be used with it. Remove the Geneve setting before downgrading firmware.
Geneve offload is used by ESX host transport nodes (the nenic driver). Check it on the host per Broadcom KB 397644:
vsish -e get /net/pNics/vmnic0/properties | grep "Driver\|Device Hard\|Device Soft"
# look for VMNET_CAP_GENEVE_OFFLOAD in "Device Hardware Cap Activated"
# vmkernel.log: "nenic: ... Geneve: Overlay offload enabled, udp_port = 6081"
Use the nenic driver and VIC firmware pair listed in the Broadcom Compatibility Guide for your ESX release. The history (nenic 1.0.35.0 on ESXi 7.0) is covered in my nenic post linked below.
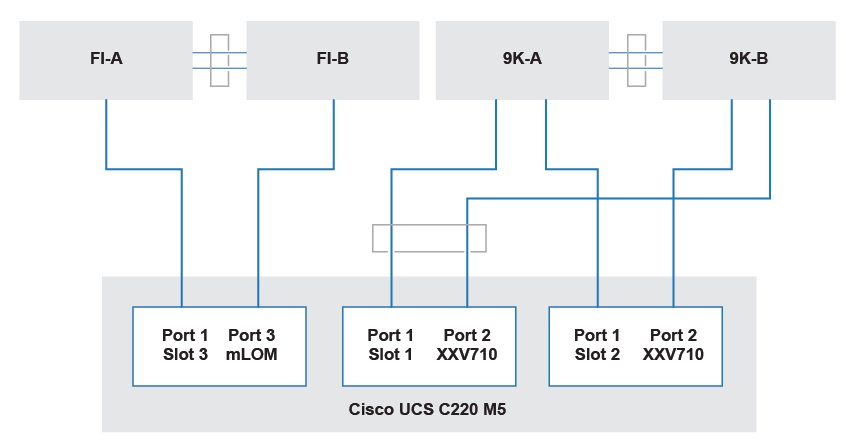
The 2021 Dell EMC VxBlock NSX-T design put the edge on a C220 M5 host. vmnic0/1 were a Cisco VIC 1457 to the FIs for management, vmnic2/3 an Intel XXV710 for TEP/overlay, and vmnic4/5 a second XXV710 for BGP peering, cabled directly to the Nexus 9000 pair. The pattern is still valid when Edge traffic should bypass the FI domain, and it fits VCF’s dedicated-host, dedicated-pNIC recommendation.
C220 M5 edge host cabling, after the Dell EMC VxBlock NSX-T design (2021)
PoC or lab: FI uplink Ethernet interfaces
For a PoC or homelab, configure FI uplink Ethernet ports for the edge VLANs and bind a vNIC template to them. For production, use the vNIC pairs described above.